



See what exposes you, fix it, prove it.
TechWatchAlert is a vulnerability and exposure management platform, built for SMBs, mid-sized companies and MSPs that do not have a full-time security team.
The problem we solve
More than 40,000 CVEs are published every year, and since April 2026 the US NVD no longer adds products and versions to most of them. Reading the feeds by hand does not scale; a tool that only reads the NVD can no longer tell who is affected. Meanwhile, NIS2 requires showing what was fixed, when, and why the rest had to wait.
Sorting is mechanical work: matching a product and a version against a list of vulnerabilities, then ranking by real exploitation. A machine does it better than a human at eight in the morning. The decision stays with your teams: what to fix first, and what can wait.
What TechWatchAlert does
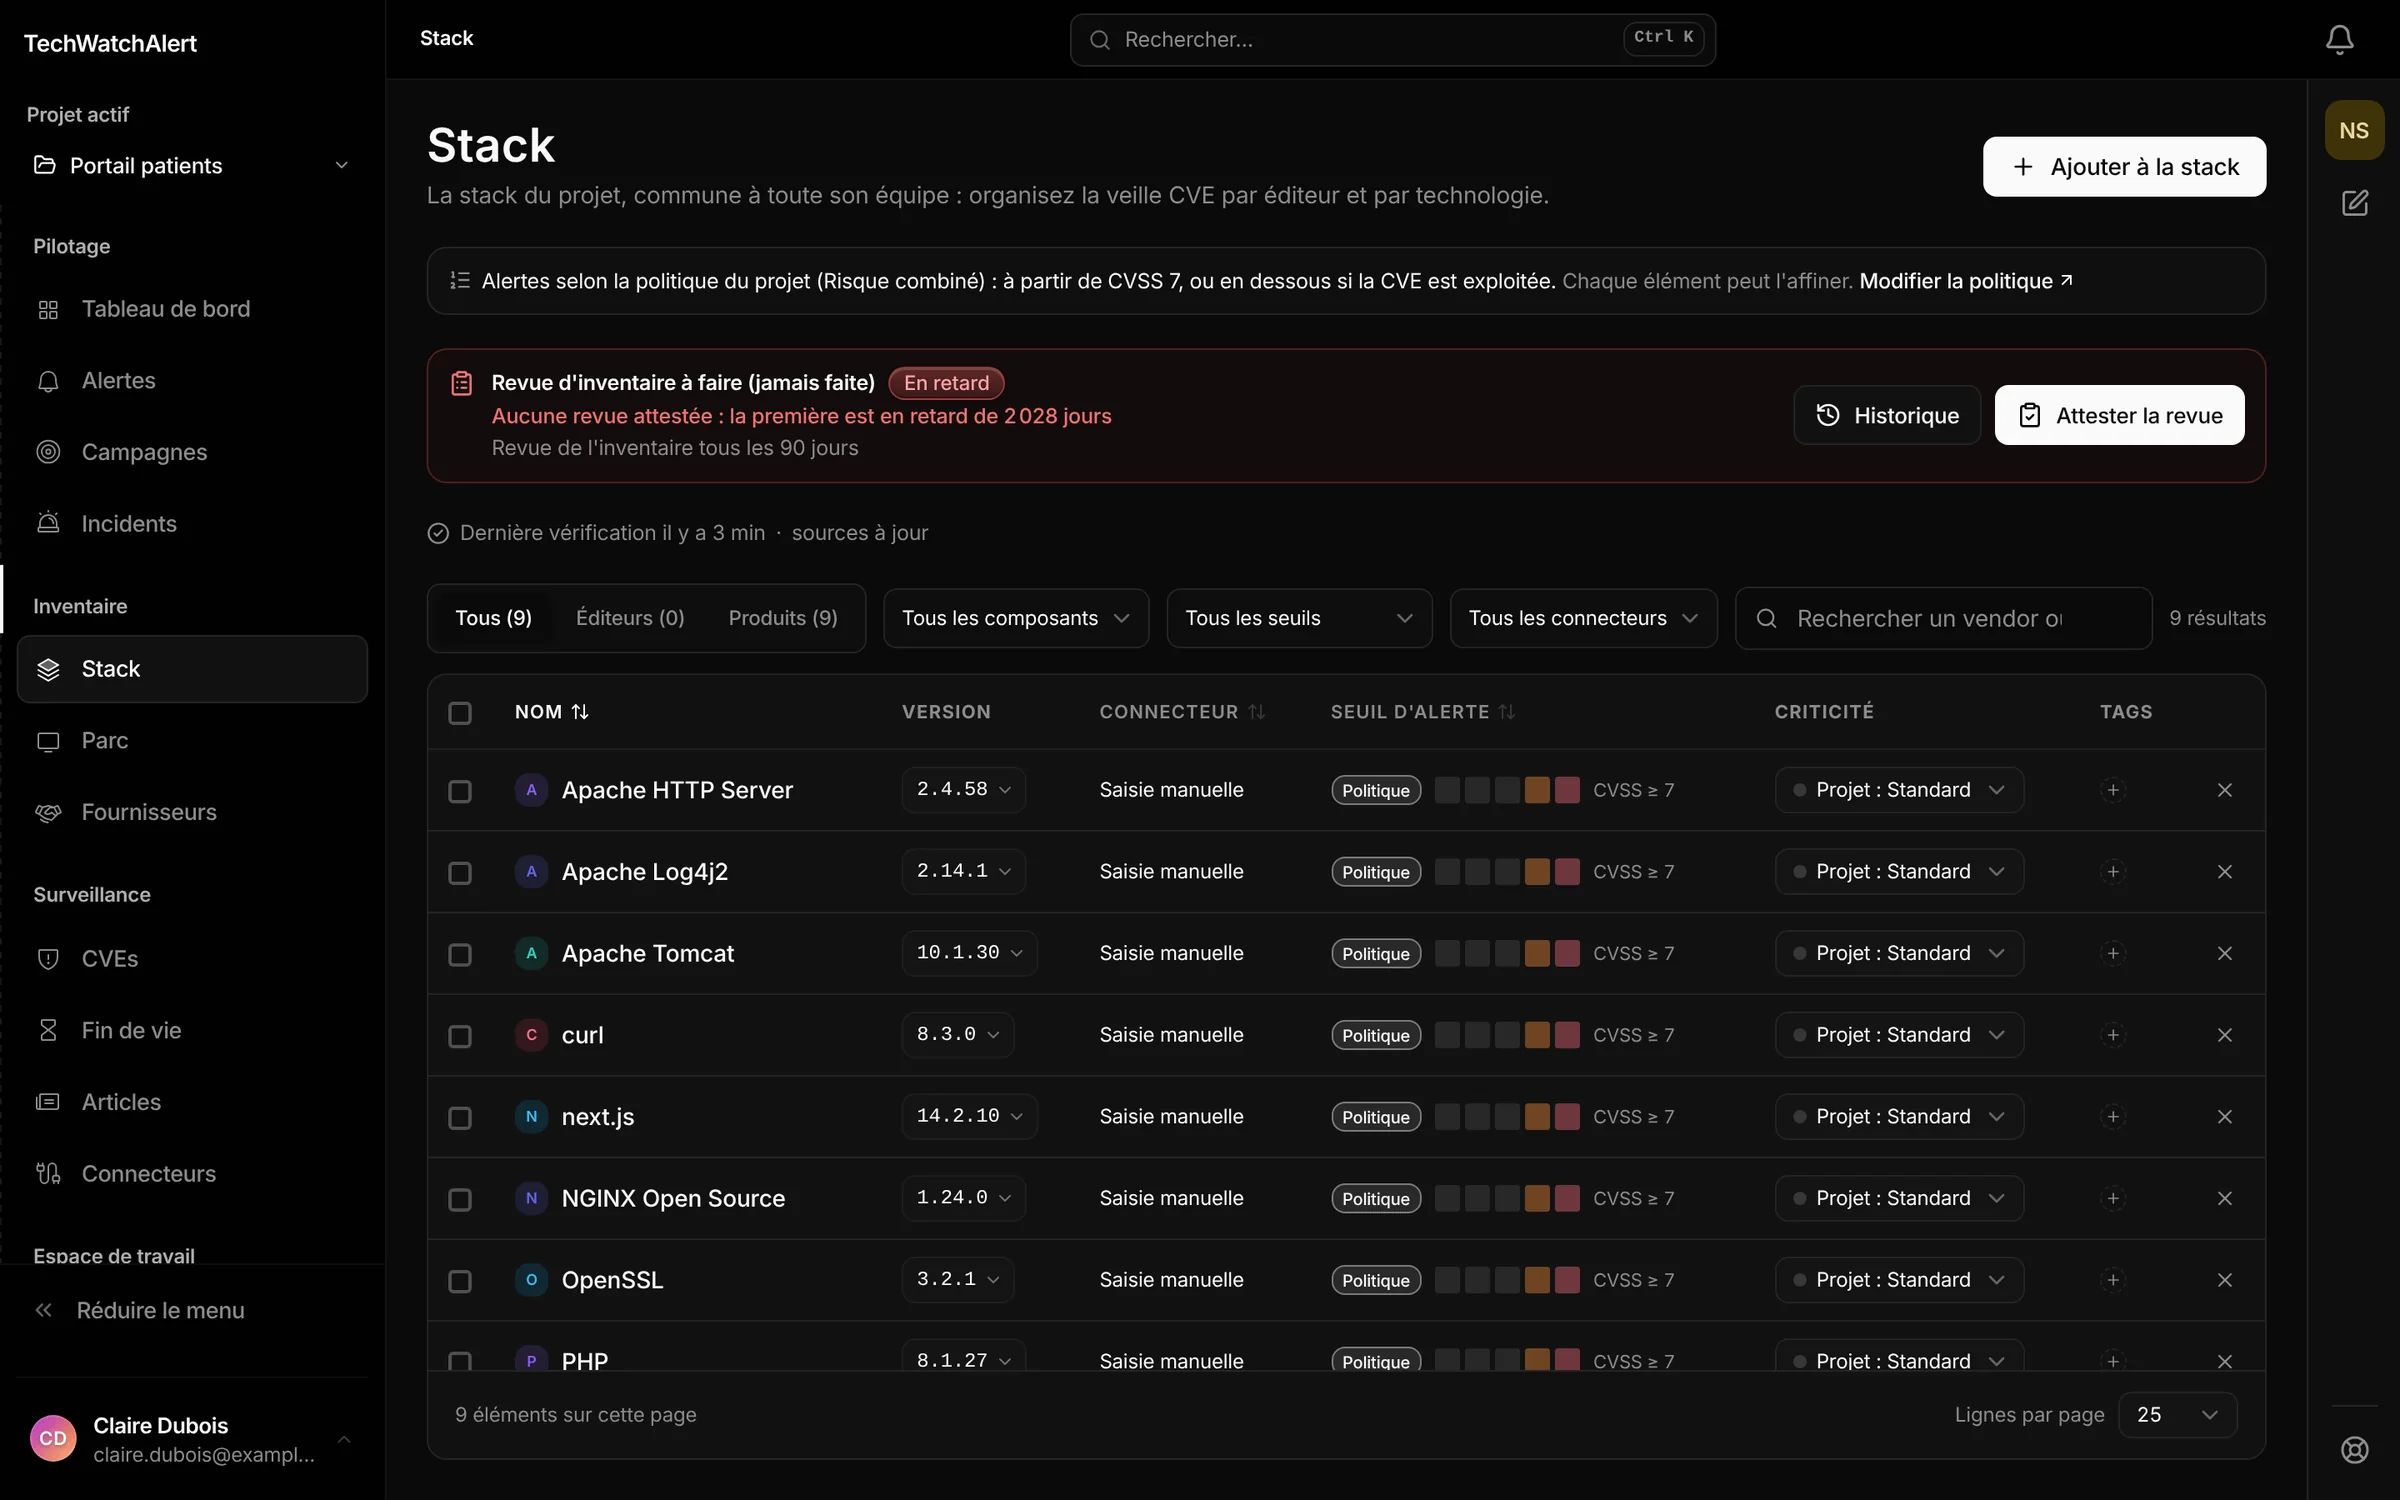
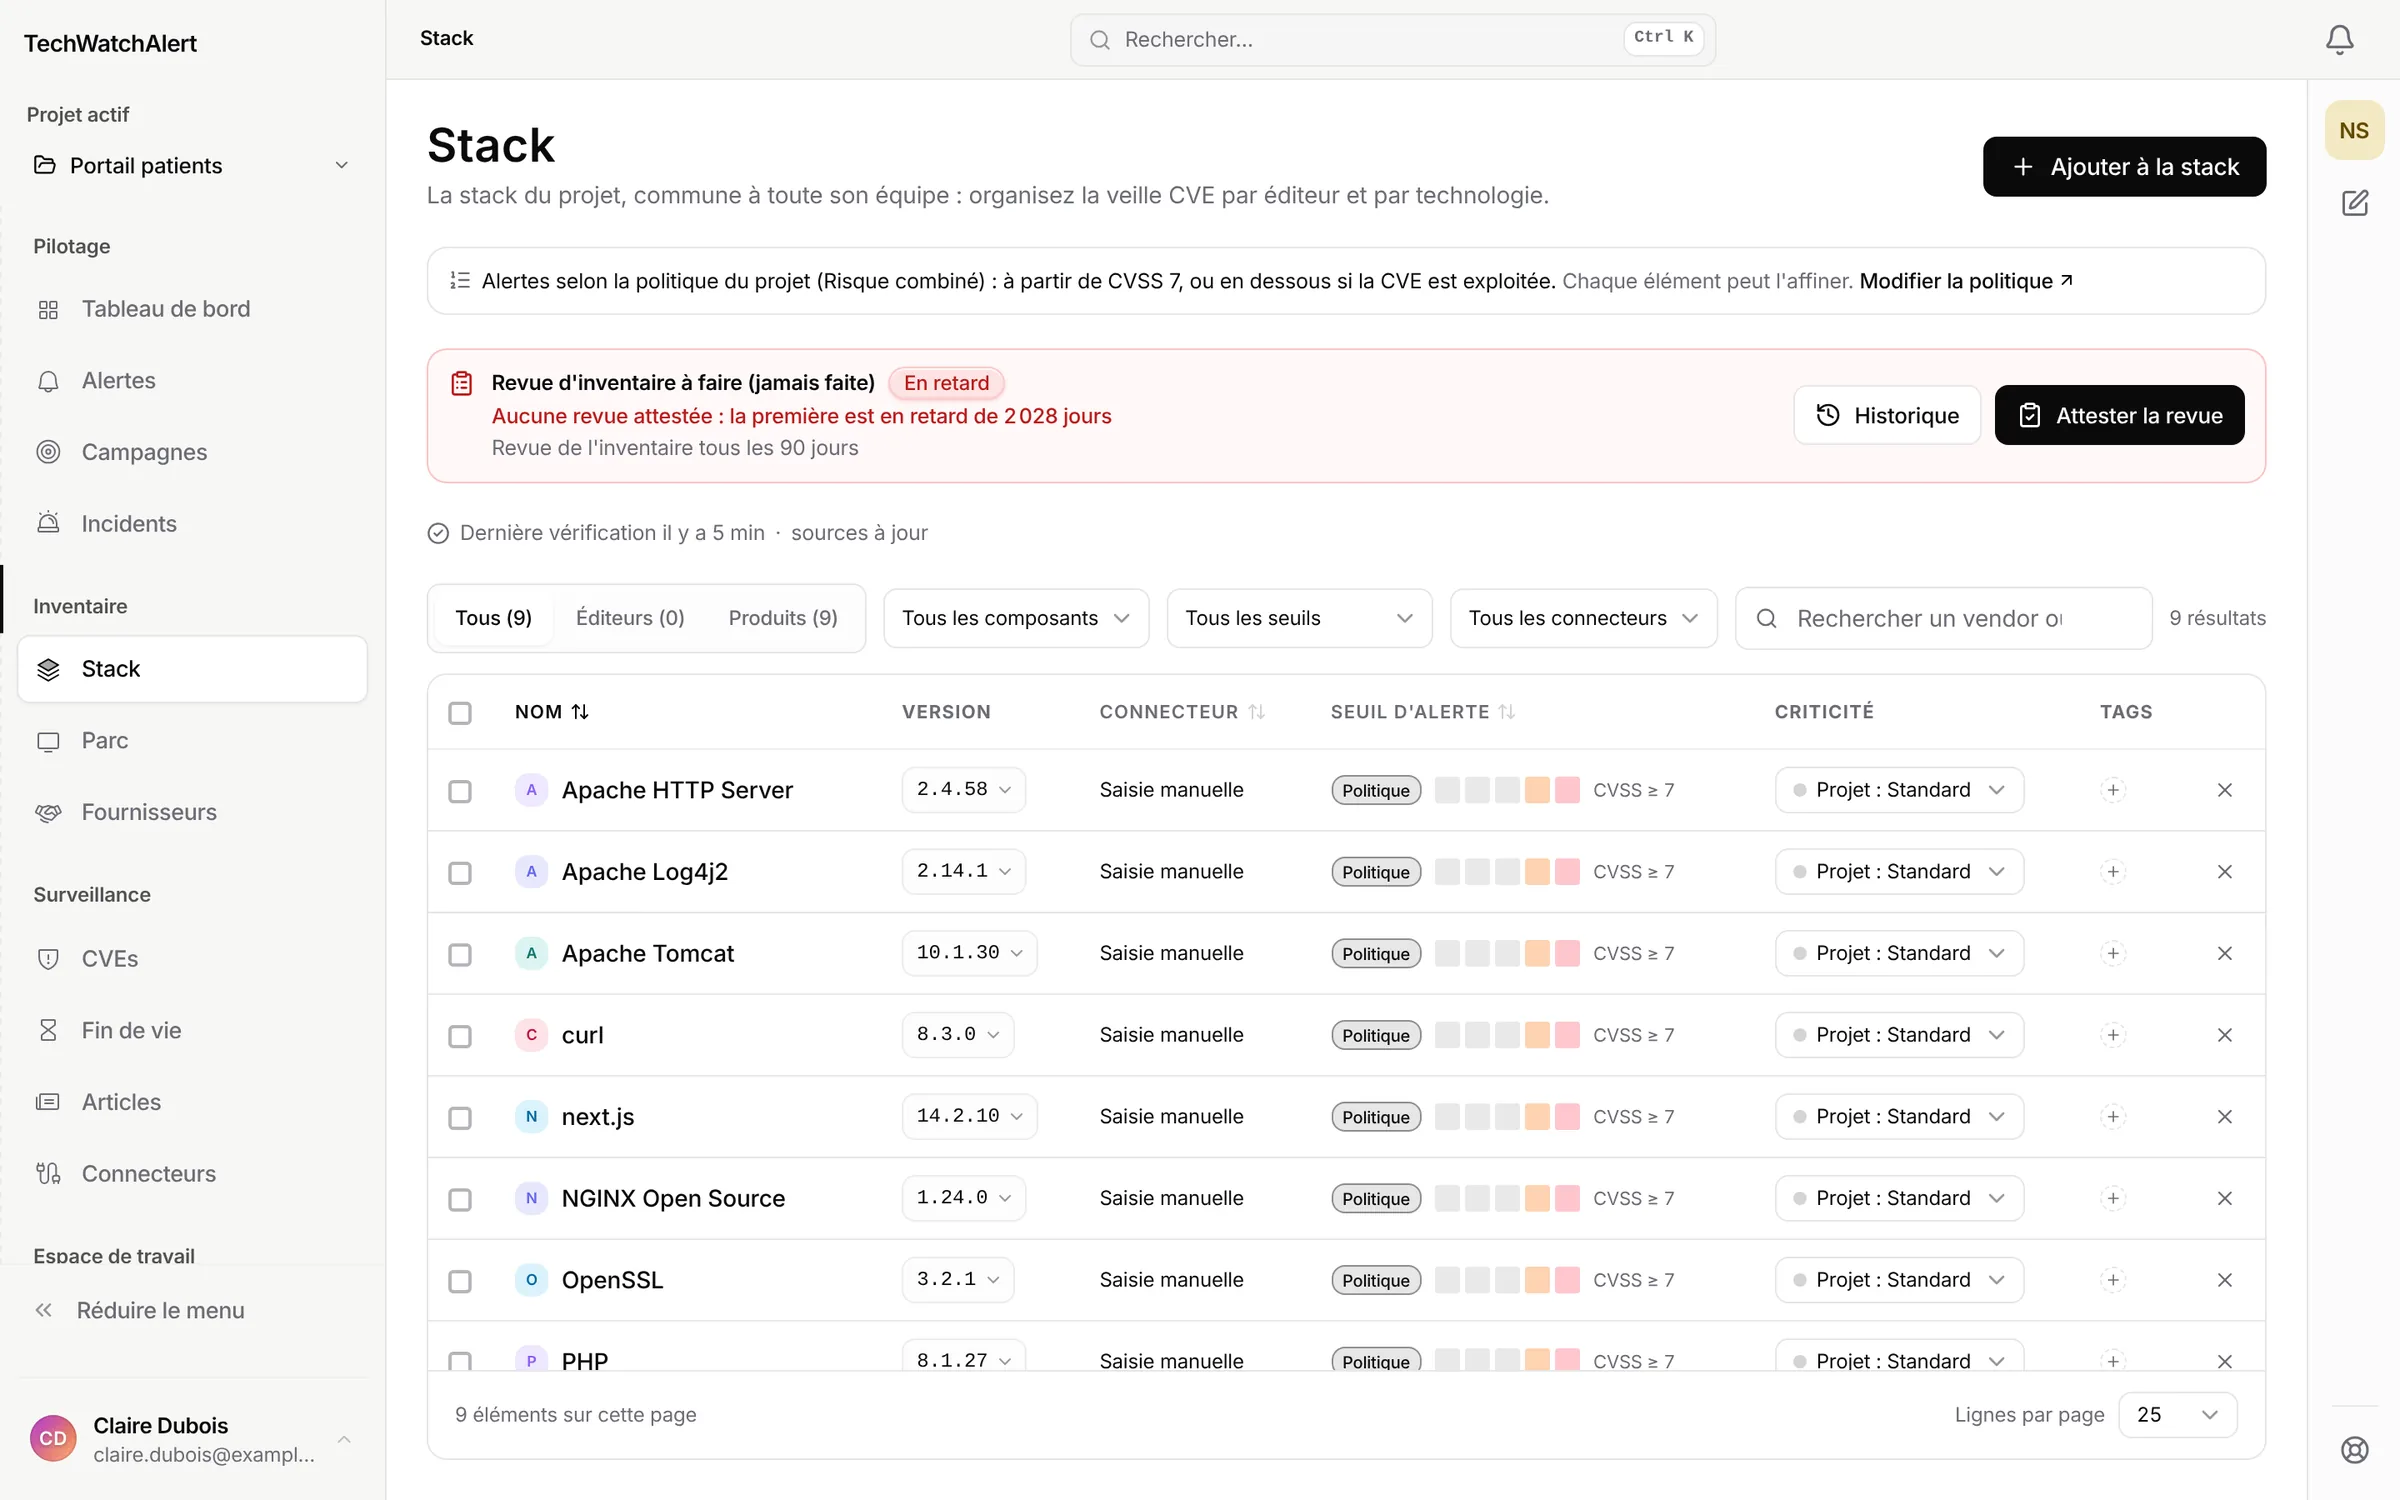
- See. The inventory comes from the agent (Windows, Linux, macOS), your repositories and SBOMs, your IT asset tools and your scanners, read through their APIs. It is matched against 19 sources, including CERT-FR, the European EUVD database and the catalogs of exploited vulnerabilities (KEV).
- Fix. Each vulnerability gets a deadline based on its exploitation; the right person is notified, a ticket goes to Jira, GitLab, GLPI or ServiceNow, and the agent installs updates in rings, within your maintenance windows (patch management).
- Prove. Decisions, deadlines and patches are dated: NIS2 and ISO 27001 reports, incident register, accepted risks, audit log (NIS2 space).
- For MSPs. All your clients in one workspace, kept apart, billed per machine, with your RMM and PSA tools (partner program).
The product is available in seven languages, with public prices, a free plan with no credit card and a 14-day trial of the Team plan.
What we don't do
We are not a network scanner: we do not probe your internal network, and the light check of your external surface only covers domains whose ownership you have proven. We do not read your code: in your repositories, only manifests and lockfiles. We are not a general-purpose compliance platform: the NIS2 workspace covers vulnerabilities, inventory, suppliers and incidents, without certification. Our comparisons say, tool by tool, when another one fits the need better.
Availability
Our availability target is 99.5% per calendar month, taken from our terms of use; the status of our services and the incident history are public on the status page. We sell neither 24/7 on-call support nor a 99.95% commitment: we only promise what we deliver.
Our commitments
- Hosted in France, subprocessors published. The application, the vulnerability database and your inventories are hosted in the Paris region, with OVHcloud. Our subprocessors, including those established outside the European Union, are named on the Security page with the safeguards that cover their transfers.
- Your data is not the product. Your inventory is used to flag what exposes you, and nothing else: no resale, no model training, no sharing. It is written in the privacy policy, with the list of subprocessors and their countries.
- Reversibility by default. You export everything, whenever you want, without writing to us and at no cost.
- Dated, sourced figures. When we publish a figure, we say where it comes from and how old it is. When we get something wrong, tell us and we fix it.